From Browser Tab to Ransomware: Encrypting Local Files with the File System Access API and Web Crypto
A malicious website can ask Chrome users to “compress photos” and, with one folder permission, encrypt every file in place using only browser APIs. No download, no extension, no native malware. This article breaks down the attack chain, the hybrid RSA/AES design, what works on Android and desktop, and what does not.
Introduction#
Ransomware usually means executables, stolen RDP sessions, or email attachments. A quieter path is emerging entirely inside the browser: a page the victim opens voluntarily can request folder access, walk every file under that directory, and overwrite them with encrypted blobs using standard APIs shipped in Chromium.
No .exe. No browser extension. No exploit for a memory corruption bug. The victim clicks Allow, picks a folder, and the tab does the rest.
This is not science fiction. It is a straight composition of:
- File System Access API (FSA):
showDirectoryPicker({ mode: "readwrite" }) - Web Cryptography API: AES-256-GCM per file, RSA-OAEP-4096 for key wrapping
The result is browser-native ransomware: encryption runs in JavaScript, keys never leave the attacker's control, and the UI can look like a harmless utility.
Threat model at a glance#
| Property | Reality |
|---|---|
| Delivery | 1-click (open URL) + 1-click (grant folder access) |
| Privilege | Same as user; limited to one granted directory tree |
| Persistence | None. Closing the tab stops the script |
| Cross-browser | Chromium only (Chrome, Edge); not Firefox/Safari |
| Context | HTTPS required (secure context) |
| User interaction | Required. Permission prompt is not bypassed |
This is user-assisted abuse, not a silent 0-click drive-by. It is still dangerous because users routinely approve "helpful" web tools without reading permission text.
The lure: social engineering beats exploits#
The most reliable part of the chain is not crypto. It is the story.
A typical lure presents itself as:
- "Compress Photo" / "AI Photo Enhancer"
- "Free up storage on your phone"
- "Batch resize your DCIM folder"
Copy is written in plain language. The victim is told to:
- Tap Start
- Select Pictures, DCIM, or Downloads
- Tap Allow when Chrome asks to access or edit files
- Keep the tab open while "compression" runs
While the progress bar says "Optimizing images…", the background loop may be encrypting every file in the tree.
Attack chain#
Victim opens HTTPS lure URL
        ↓
Clicks "Start" → showDirectoryPicker({ mode: "readwrite" })
        ↓
Chrome prompt: "Allow this site to view/edit files?"
        ↓
Victim selects folder (e.g. DCIM, Documents)
        ↓
JavaScript recursively enumerates files (FileSystemHandle)
        ↓
For each file:
  - Generate random AES-256-GCM key
  - Encrypt file contents
  - Wrap AES key with attacker RSA public key
  - Overwrite original via createWritable()
        ↓
Optional: display ransom note / fake "done" screenRead-only mode (mode: "read") still enables reconnaissance and selective exfiltration. Encrypting in place requires readwrite.
Technical core: hybrid encryption in the browser#
Each file is encrypted independently:
- AES-256-GCM encrypts the file body (fast, suited to large blobs).
- A random 12-byte IV is generated per file.
- The raw AES key is encrypted with the attacker's RSA-OAEP-4096 public key (SHA-256).
- The encrypted payload replaces the original file in place through
FileSystemFileHandle.createWritable().
On-disk layout (conceptual):
[4 bytes: RSA ciphertext length, big-endian]
[RSA-OAEP encrypted AES key]
[12 bytes: GCM IV]
[AES-GCM ciphertext]The RSA private key never enters the page. Only the SPKI public key (base64) is embedded or fetched from /config.json. Without the private key, recovery is intended to be infeasible.
A victim ID (random UUID fragment) can be uploaded to the operator server so payments map to the correct key escrow workflow in a lab scenario.
Minimal encryption logic (illustrative)#
async function encryptFileHandleInPlace(fileHandle, rsaPublicKey) {
  const file = await fileHandle.getFile();
  const plaintext = await file.arrayBuffer();

  const aesKey = await crypto.subtle.generateKey(
    { name: "AES-GCM", length: 256 },
    true,
    ["encrypt", "decrypt"]
  );
  const iv = crypto.getRandomValues(new Uint8Array(12));
  const ciphertext = await crypto.subtle.encrypt(
    { name: "AES-GCM", iv },
    aesKey,
    plaintext
  );

  const rawAesKey = await crypto.subtle.exportKey("raw", aesKey);
  const encryptedAesKey = await crypto.subtle.encrypt(
    { name: "RSA-OAEP" },
    rsaPublicKey,
    rawAesKey
  );

  const payload = buildPayload(encryptedAesKey, iv, ciphertext);
  const writable = await fileHandle.createWritable();
  await writable.write(payload);
  await writable.close();
}Directory traversal uses async generators over dirHandle.values(), recursing into subdirectories. The pattern matches a legitimate batch photo tool.
Platform matrix#
| Platform | FSA readwrite | Web Crypto | Practical? |
|---|---|---|---|
| Chrome Android 132+ | Yes | Yes | Primary mobile target |
| Chrome / Edge desktop | Yes | Yes | Windows, macOS, Linux |
| Firefox | No FSA | Yes | Not viable for this chain |
| Safari (iOS/macOS) | No FSA | Yes | Not viable |
| In-app WebViews | Often broken/limited | Varies | Unreliable |
Attack pages commonly User-Agent gate non-Chromium browsers to a maintenance screen so victims do not hit broken flows that expose the ruse.
Beyond encryption: recon and on-demand exfil#
The same FSA permission enables lighter modes:
- Manifest upload: file paths and sizes sent to a server before any encryption
- Operator dashboard: attacker cherry-picks files; victim tab polls and uploads on demand
- Live session control: stop/finish signals while the tab stays open
Encryption and exfil can run in parallel: the victim sees "compression in progress" while both pipelines execute.
Hosting the lure on a CDN (e.g. Vercel) while the operator backend runs on a tunnel is a common split architecture. The static site delivers the story. The tunnel receives data and keys.
What this is not#
Clarifications for defenders and journalists:
- Not a Chrome 0-day: documented APIs used as designed.
- Not silent: explicit folder permission required.
- Not full-disk: scope is the chosen directory subtree.
- Not persistent: no registry, cron, or startup folder.
- Not unstoppable: closing the tab halts further damage; already-written ciphertext remains.
Detection and response hints#
User-visible indicators:
- Chrome prompt mentioning view or edit files on an unrelated site
- Files become unreadable; entropy looks like encrypted blobs
- Original extensions may remain or appear unchanged despite corruption
Enterprise / SOC:
- Unusual long-lived HTTPS sessions with large outbound POST bodies (exfil mode)
Victim response:
- Disconnect network; close the tab
- Do not pay without verifying key recovery
- Restore from offline backup if available
- Report URL to hosting provider and national CSIRT (BSSN)
Working PoC: Chrome-Spysimple#
This is not a theoretical chain. It has been built and exercised end-to-end as an authorized lab PoC: Chrome-Spysimple.
The project implements a complete operator workflow behind a fake Compress Photo / AI Photo Enhancer lure:
- Recon mode (
read): victim grants folder access; the tab uploads a file manifest; the operator browses the tree from a dashboard and cherry-picks files for on-demand exfil. - Encryption mode (
readwrite --crypto): same lure UI, but a background loop overwrites each file in place with the RSA+AES blob format described above. - Operator dashboard: live sessions, fetch queue, progress, stop/finish signals, and download links for exfiltrated files.
- Local decryptor:
decryptor.htmlplus the server-side private key restores files after lab testing. - Split deployment: static lure on Vercel (downsize-files.vercel.app) with Chromium-only UA gate; backend and dashboard run via HTTPS tunnel.
In a controlled test, the victim sees a normal photo utility. The operator sees real folder contents within seconds of permission grant. With crypto enabled, ciphertext is written before the fake "done" screen appears. That is the practical difference between "browser APIs exist" and "browser APIs deployed as ransomware."
Additional notes (UniAI discussion)#
Separate from the PoC above, a public UniAI thread walks through the same API pairing from a standalone HTML perspective: Ransomware / UniAI (shared conversation).
That discussion is useful background if you want to understand adjacent details not covered step-by-step in this article:
- Self-contained
ransomware.htmlanddecryptor.htmlsamples (single file, no server) - RSA-4096 keypair generation via browser DevTools console
- Step-by-step attack flow table from first visit through ransom note and recovery
- Notes on private key custody: keeping the PKCS8 key offline, Grok as key oracle, or a backend
/decryptendpoint - Trade-offs such as writing
.encalongside originals vs deleting originals withfileHandle.remove()
Think of UniAI as supplementary walkthrough material. Chrome-Spysimple is the reproducible lab case with server, dashboard, and multi-mode operation.
Research and ethics#
This technique belongs in authorized lab environments: red team with scope, academic PoC, or defensive replication. Deploying against systems without permission is illegal in most jurisdictions.
Building the PoC teaches:
- How far legitimate web platform features extend into the host file system
- Why permission prompt copy is a security boundary users must understand
- Why backup strategy remains the last line of defense against client-side encryption
Conclusion#
Browser ransomware is not a new vulnerability class. It is a capability merge: File System Access plus Web Crypto turns a phishing page into a file-encrypting agent. Chromium on Android and desktop is the main exposure surface today.
The fix is not only patch Tuesday. It is user education, permission hygiene, backup discipline, and continued pressure on browsers to make write access scary, specific, and revocable.
For defenders, the question is no longer "Can web pages still only read cookies?" but "What happens when a web page can rewrite your Documents folder, and the user said yes?"
Technical analysis based on File System Access API and Web Cryptography API behavior in Chromium. For authorized security research and education only.
Continue exploring
Related articles
Research
Jejak Identitas Indonesia dalam Bisnis KYC Claude
Foto pertemuan, dua video, percakapan forum, dan penawaran jasa menuntun penelusuran atas dugaan pemanfaatan identitas warga Indonesia untuk verifikasi akun Claude.
Research
From Moodle Assignment Upload to Ghostscript Code Execution
How a memory error in Ghostscript can affect Moodle assignment conversion. The latest Moodle release can still be exposed if its server uses a vulnerable Ghostscript installation.
Technology
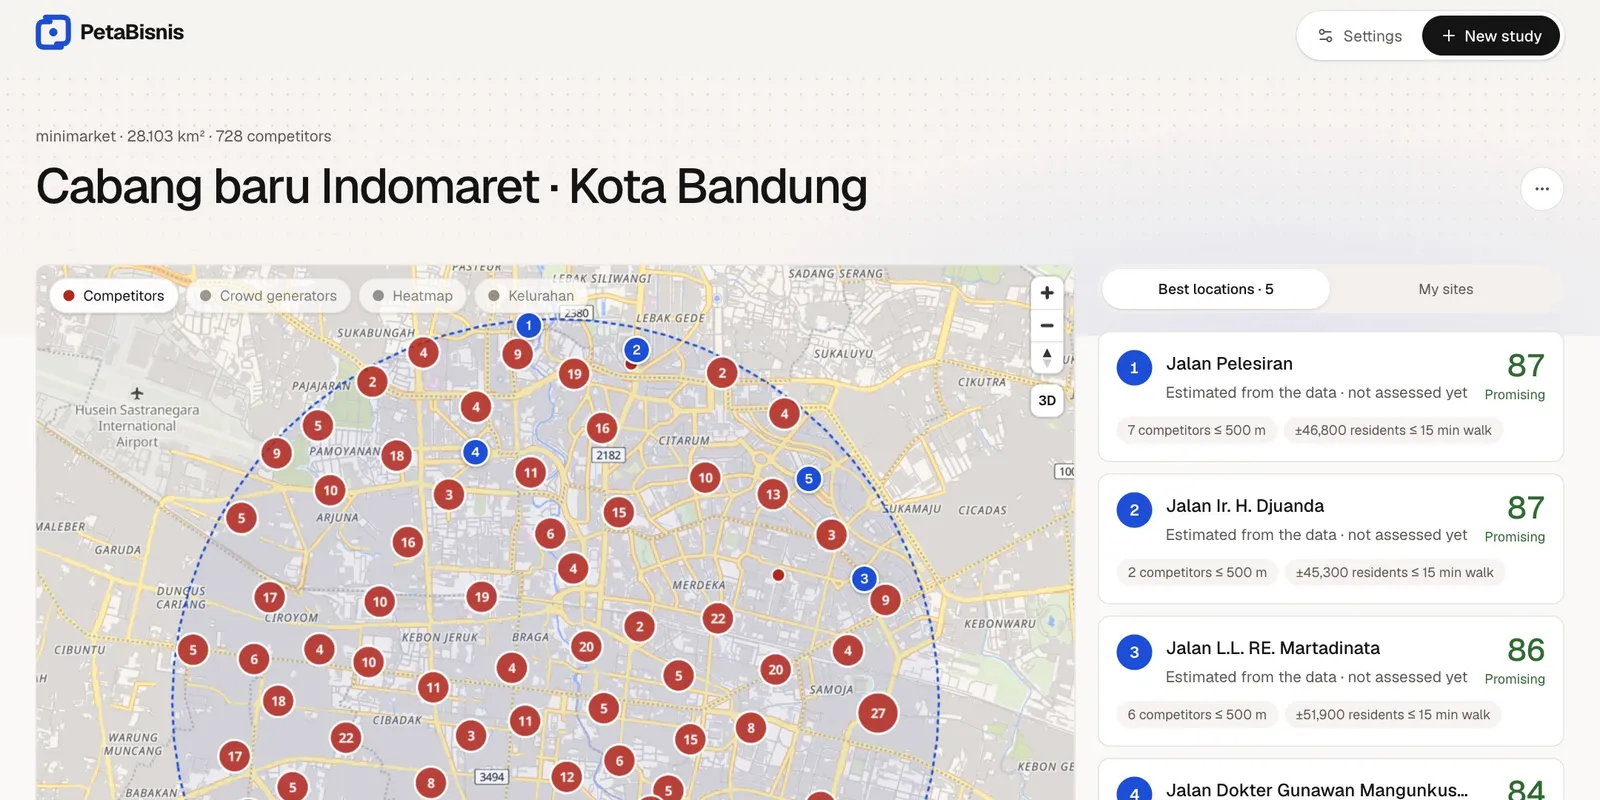
PetaBisnis: Choose a Business Location with Data
Before renting a place for a new shop, owners need to know where the competitors are, how busy the area is, and what the risks are. PetaBisnis answers these questions with a location study for any area in Indonesia.